
Enterprise reporter & Cyber correspondent, BBC Information
 BBC
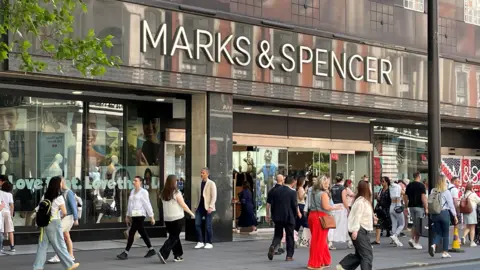
Marks & Spencer has revealed that some private buyer information was stolen within the latest cyber assault, which may embody phone numbers, house addresses and dates of delivery.
The Excessive Avenue big mentioned the private info taken may additionally embody on-line order histories, however added the information theft didn’t embody useable cost or card particulars, or any account passwords.
M&S was hit by the cyber assault three weeks in the past and is struggling to get providers again to regular, with on-line orders nonetheless suspended.
The retailer mentioned prospects could be prompted to reset account passwords “for further peace of thoughts”.
M&S chief govt Stuart Machin mentioned the corporate was writing to prospects to tell them that “sadly, some private buyer info has been taken”.
“Importantly, there isn’t any proof that the data has been shared,” he added.
Nonetheless, it’s understood that the hackers may but share or promote on the stolen information as a part of their makes an attempt to extort M&S, which nonetheless represents a danger of identification fraud.
The retailer has not revealed what number of of its prospects have had their information stolen, however mentioned it had emailed all web site customers to tell them, reported the case to the related authorities and was working with cyber safety specialists to watch any developments.
In keeping with its final full-year outcomes, the corporate had some 9.4 million energetic on-line prospects within the 12 months to 30 March.
Mr Machin mentioned M&S was “working across the clock to get issues again to regular” as rapidly as doable.
What has been taken?
M&S confirmed the contact info stolen may embody:
- identify
- date of delivery
- phone quantity
- house handle
- family info
- electronic mail handle
- on-line order historical past
The retailer added any card info taken wouldn’t be useable because it doesn’t maintain full card cost particulars on its programs.
What do you have to do?
M&S has mentioned folks don’t must take any motion, however has additionally mentioned:
- customers might be prompted to reset their password for his or her on-line account
- prospects must be cautious as they “may obtain emails, calls or texts claiming to be from M&S when they don’t seem to be”
- M&S won’t ever contact you and ask for private account info like usernames or passwords
Lisa Barber, tech editor at shopper group Which?, mentioned it was regarding that criminals had gained entry to info that might be used for identification fraud.
“It is all the time a good suggestion to alter your password as quickly as doable if there’s been a safety breach and to make sure your new password is exclusive from another on-line accounts,” she mentioned.
Matt Hull, head of menace intelligence at cyber safety firm NCC Group, mentioned attackers who’ve stolen private info can use it to “craft very convincing scams”.
“If you happen to’re uncertain about an electronic mail’s authenticity, do not click on any hyperlinks. As a substitute, go to the corporate’s web site on to confirm any claims.”
How did the hack occur?
Issues at M&S started over the Easter weekend when prospects reported issues with Click on & Accumulate and contactless funds in shops.
The corporate confirmed it was coping with a “cyber incident” and whereas in-store providers have resumed, its on-line orders on its web site and app have been suspended since 25 April.
There may be nonetheless no phrase on when on-line orders will resume.
M&S’ announcement that buyer information had been stolen as a part of the continuing cyber assault was anticipated because of the nature of the assault.
The hackers behind it, who additionally just lately focused Co-op and Harrods, used the DragonForce cyber crime service to hold out the assaults.
DragonForce operates an affiliate cyber crime service on the darknet for anybody to make use of their malicious software program and web site to hold out assaults and extortions.
The group is understood to make use of a double extortion technique, which suggests they steal a duplicate of their sufferer’s information in addition to scramble it to make it unusable.
They will then successfully ask for a ransom for each unscrambling the information and deleting their copy.
Nonetheless, if the individual or enterprise hacked doesn’t need to pay a ransom, criminals can in some instances begin leaking the stolen information to different cyber criminals, who may look to hold out additional assaults to realize extra delicate information.
For the time being, DragonForce’s darknet web site doesn’t have any entries about M&S.
‘It is costing them fortunes’
Jackie Naghten, a enterprise marketing consultant who has labored with huge retailers together with M&S, Arcadia and Debenhams, informed the BBC that the hierarchy at M&S could be taking the information breach “very significantly”, however warned trendy logistics in retail have been “massively advanced”.
“I really feel they’ve been protecting their powder dry. In the event that they haven’t acquired something optimistic to say then they don’t seem to be saying something,” she mentioned.
Ms Naghten mentioned on the entire prospects have been exhibiting numerous assist and sympathy to the retailer.
However she added it was probably M&S had “one other week” earlier than it must present info on when regular service would resume.
“It is completely costing them fortunes,” she informed the BBC.
Shares in M&S are down some 12% over the previous month.
[ad_2]