
Know-how Reporter
 Bugcrowd
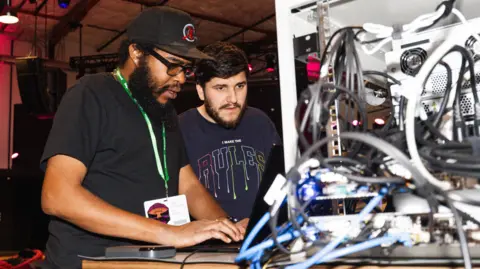
Few expertise careers provide the possibility to reveal your abilities in unique venues worldwide, from luxurious inns to Las Vegas e-sports arenas, friends cheering you on as your title strikes up the leaderboard and your earnings rack up.
However that is what Brandyn Murtagh skilled inside his first yr as a bug bounty hunter.
Mr Murtagh received into gaming and constructing computer systems at 10 or 11-years-old and at all times knew “I wished to be a hacker or work in safety”.
He started working in a safety operations centre at 16, and moved into penetration testing at 20, a job that additionally concerned testing the safety of purchasers’ bodily and laptop safety: “I needed to forge false identities and break into locations after which hack. Fairly enjoyable.”
However previously yr he has grew to become a full-time bug hunter and unbiased safety researcher, that means he scours organizations’ laptop infrastructure for safety vulnerabilities. And he hasn’t seemed again.
Web browser pioneer Netscape is considered the primary expertise firm to supply a money “bounty” to safety researchers or hackers for uncovering flaws or vulnerabilities in its merchandise, again within the Nineties.
Finally platforms like Bugcrowd and HackerOne within the US, and Intigriti in Europe, emerged to attach hackers and organizations that wished their software program and methods examined for safety vulnerabilities.
As Bugcrowd founder Casey Ellis explains, whereas hacking is a “morally agnostic talent set”, bug hunters do must function inside the legislation.
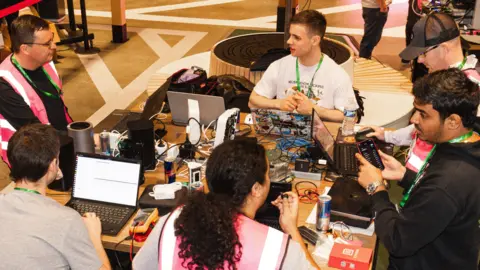
Platforms like Bugcrowd convey extra self-discipline to the bug-hunting course of, permitting corporations to set the “scope” of what methods they need hackers to focus on. They usually function these reside hackathons the place high bug hunters compete and collaborate “hammering” methods, displaying off their abilities and probably incomes massive cash.
The payoff for corporations utilizing platforms like Bugcrowd can be clear. Andre Bastert, international product supervisor AXIS OS, at Swedish community digicam and surveillance tools agency Axis Communications, stated that with 24 million traces of code in its machine working system, vulnerabilities are inevitable. “We realized it is at all times good to have a second set of eyes.”
Platforms like Bugcrowd imply “you should utilize hackers as a pressure for good,” he says. Since opening its bug bounty programme, Axis has uncovered – and patched – as many as 30 vulnerabilities, says Mr Bastert, together with one “we deem very extreme”. The hacker accountable obtained a $25,000 (£19,300) reward.
 Bugcrowd
So, it may be profitable work. Bugcrowd’s high incomes hacker over the past yr earned over $1.2m.
However whereas there are hundreds of thousands of hackers registered on the important thing platforms, Inti De Ceukelaire, chief hacking officer at Intigriti, says the quantity looking on a each day or weekly foundation is “tens of hundreds.” The elite tier, who’re invited to the flagship reside occasions might be smaller nonetheless.
Mr Murtagh says: “A very good month would appear like a few crucial vulnerabilities discovered, a few highs, quite a lot of mediums. Some good pay days in a great state of affairs.” However he provides, “It would not at all times occur.”
But with the explosion of AI, bug hunters have entire new assault surfaces to discover.
Mr Ellis says organizations are racing to achieve a aggressive benefit with the expertise. And this sometimes has a safety affect.
“Usually, for those who implement a brand new expertise rapidly and competitively, you are not considering as a lot about what would possibly go flawed.” As well as, he says, AI isn’t just highly effective however “designed for use by anybody”.
Dr Katie Paxton-Worry, a safety researcher and cybersecurity lecturer at Manchester Metropolitan College, factors out that AI is the primary expertise to blow up onto the scene with the formal bug looking group already in place.
And it has levelled the taking part in area for hackers, says Mr De Ceukelaire. Hackers – each moral and never – can exploit the expertise to hurry up and automate their very own operations. This ranges from conducting reconnaissance to establish susceptible methods, to analysing code for flaws or suggesting potential passwords to interrupt into methods.
However trendy AI methods’ reliance on massive language fashions additionally means language abilities and manipulation are an necessary a part of the hacker device equipment, Mr De Ceukelaire says.
He says he has drawn on basic police interrogation methods to befuddle chatbots and get them to “crack”.
Mr Murtagh describes utilizing such social engineering methods on chatbots for retailers: “I might try to make the chatbot trigger a request and even set off itself to provide me one other person’s order or one other person’s information.”
 Getty Pictures
However these methods are additionally susceptible to extra “conventional” net app methods, he says. “I’ve had some success in an assault known as cross website scripting, the place you may primarily trick the chatbot into rendering a malicious payload that may trigger all types of safety implications.”
However the risk would not cease there. Dr Paxton-Worry says an over-focus on chatbots and huge language fashions can distract from the broader interconnectedness of AI powered methods.
“For those who get a vulnerability in a single system, the place does that finally seem in each different system it connects to? The place are we seeing that hyperlink between them? That is the place I might be searching for these sorts of flaws.”
Dr Paxton-Worry provides that there hasn’t been a serious AI-related information breach but, however “I believe it is only a matter of time”.
Within the meantime, the burgeoning AI business must be certain it embraces bug hunters and safety researchers, she says. “The truth that some corporations do not makes it a lot tougher for us to do our job of simply protecting the world protected.”
That’s unlikely to place off the bug hunters within the meantime. As Mr De Ceukelaire says: “As soon as a hacker, at all times a hacker.”
[ad_2]
